 FR
 EN
Manage your certificates Microsoft ADCS from a single interface.
Certyra centralises the inventory, monitoring and lifecycle of every certificate issued by your Microsoft Active Directory Certificate Services authorities: expiry alerts, issuance, renewal, revocation, reporting and audit.
Centralised management of one or more Microsoft ADCS certificate authorities within a single Active Directory domain.
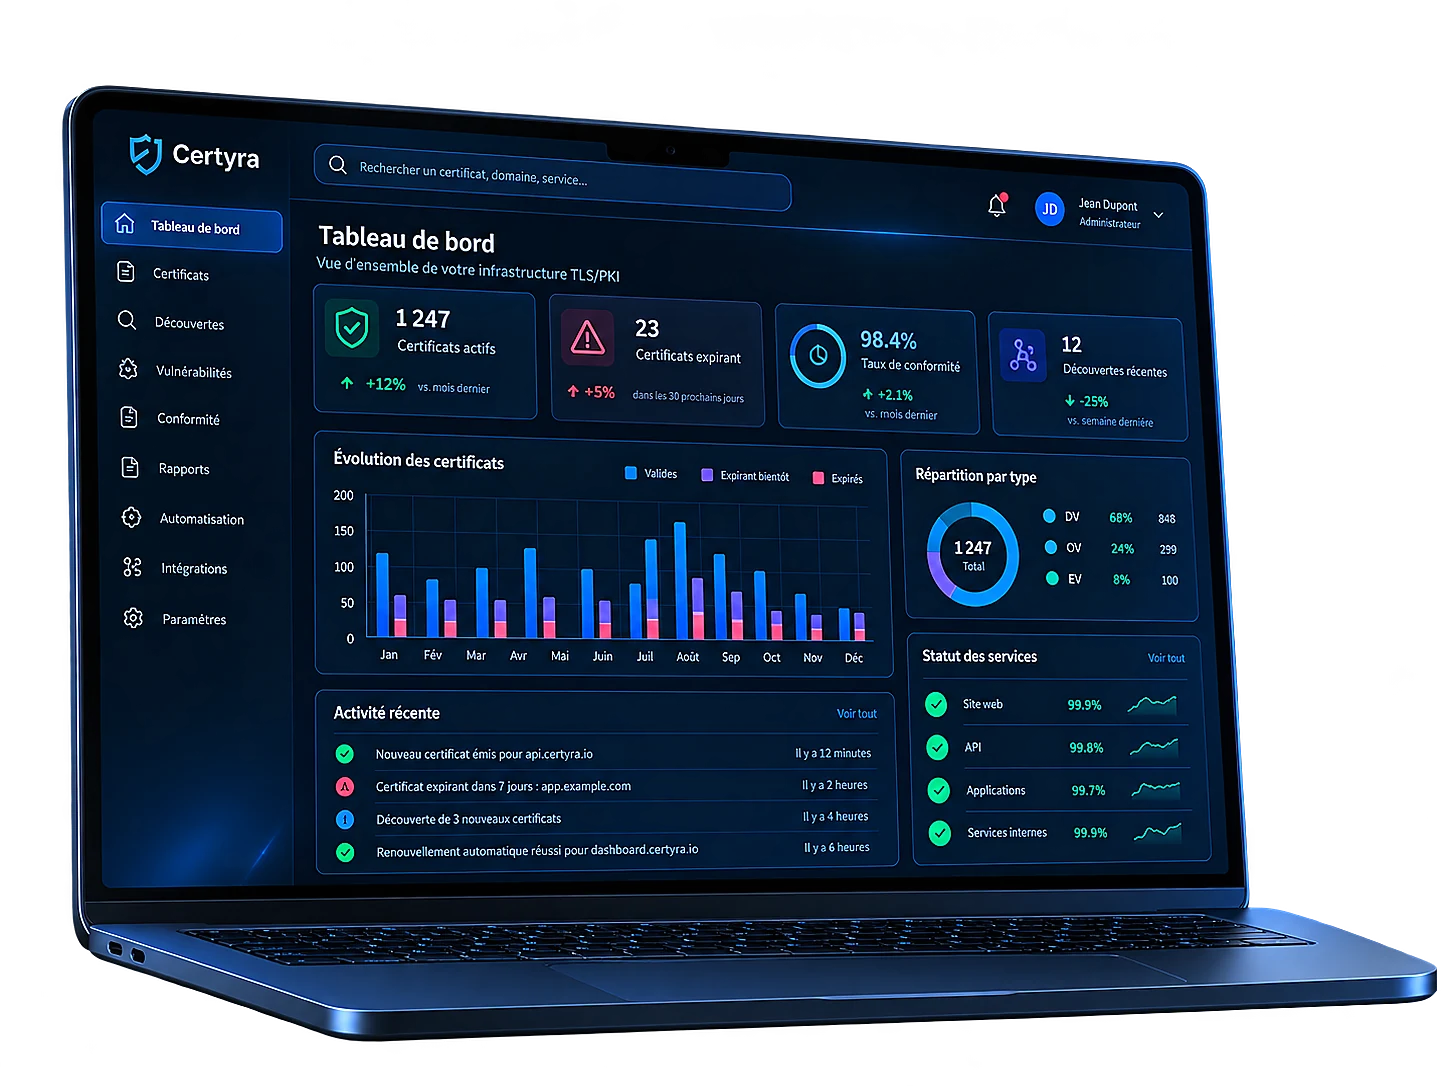
A clear view, even for the largest environments.
The problem
A Microsoft PKI issues your certificates. Running them over time is another matter.
As the estate grows, certificates spread across authorities, templates, applications and teams. Without a dedicated monitoring tool, simple questions become hard to answer quickly — at the expense of service continuity and compliance.
Which certificates are about to expire?
Spotting them early enough allows renewal to be planned before a service is affected.
What is actually being monitored?
Listing certificates is not enough. You also need to know which are covered by a rule and which are left unwatched.
Can past operations be traced?
Issuance, renewal, revocation, approval: every sensitive action must be attributable, dated and tied to its authority.
Security and audit requirements aligned with ANSSI good practice. Certyra helps you demonstrate control over your certificates and the robustness of your PKI, with detailed audit logs and full traceability of operations.
ANSSIFrench national cybersecurity agencyThe Certyra solution
From inventory to revocation: manage the whole lifecycle from one tool.
Certyra complements Microsoft ADCS without replacing it. It adds a management layer to inventory certificates, define what must be monitored, anticipate expiry, carry out the main lifecycle operations and keep their trail.
Inventory and monitoring
Automatic discovery of certificates, advanced filtering, customisable monitoring rules and real-time alerts.
Lifecycle
Issuance, renewal and revocation from the interface, with approval of pending requests.
Reporting and compliance
Dashboards, detailed reports, exports and audit log for your compliance needs.
Fits your infrastructure
Installed on your servers, compatible with your Active Directory and your existing processes.
Lifecycle
A simple, complete process.
From discovery to revocation, Certyra supports every stage with the right tools and full traceability.
Discover and centralise all your certificates.
Set rules and get alerted.
Carry out operations safely.
Withdraw a certificate when needed.
Keep a complete trail of every action.
Why choose Certyra?
Why choose Certyra for Microsoft ADCS?
Built for IT, security and infrastructure teams who want to keep control of their PKI.
Advanced ADCS certificate monitoring
Watch every certificate with rules that match your usage, proactive alerts and a consolidated view across all your services and environments.
Visibility over your estate
Get a clear, reliable view of your certificates: authorities, templates, states, expiry, assignments and usage. Spot blind spots and reduce the risk of outage.
Audit log and compliance
Trace every operation and produce reports ready for internal or external audits. Certyra eases compliance with regulatory requirements and ANSSI recommendations.
100% on-premise architecture
Your data stays inside your information system. Certyra installs on your Windows servers and integrates natively with Active Directory, with no cloud dependency.
Editions
Editions that fit your environment.
From the smallest to the largest environment, choose the edition that matches your estate and your needs.
Small environments
One authority, an estate under control
- E-mail expiry alerts
- Reports and audit log
Growing environments
The estate expands, monitoring follows
- ANSSI compliance
- Full audit and extended retention
Multi-site environments
Several authorities, one console
- Multi-authority management
- External API
Large environments
High volume and integrations
- Multi-authority management
- External API
Critical environments
No limits, with dedicated support
- Unlimited number of authorities
- Dedicated support
The detail, edition by edition
The full core is present from edition S. ANSSI compliance opens at M, and multi-authority management with the external API from L.
Swipe the table to compare editions
| S | M | L | XL | XXL | |
|---|---|---|---|---|---|
| Volumes | |||||
| Monitored certificates | 1,000 | 7,500 | 30,000 | 100,000 | unlimited |
| Certificate authorities | 1 | 1 | 3 | 5 | unlimited |
| Monitoring rules | 10 | 25 | unlimited | unlimited | unlimited |
| Discovery and inventory | |||||
| Complete estate inventory | |||||
| Automatic ADCS synchronisation | |||||
| Multi-criteria search | |||||
| Duplicate detection | |||||
| Tagging | |||||
| Multi-authority inventory | |||||
| Consolidated view across authorities | |||||
| Filter by authority | |||||
| Certificate lifecycle | |||||
| Certificate issuance | |||||
| Renewal | |||||
| Revocation | |||||
| Approval workflow | |||||
| Separation of duties | |||||
| Template management | |||||
| Template publication | |||||
| Bulk CSV import | |||||
| Issuance targeted per authority | |||||
| Multi-authority bulk import | |||||
| Templates per authority | |||||
| Monitoring and alerts | |||||
| Declarative monitoring rules | |||||
| Expiry alerts | |||||
| E-mail notifications (9 types) | |||||
| Customisable message templates | |||||
| Configurable thresholds | |||||
| Rules per authority | |||||
| Alerts per authority | |||||
| Security and compliance | |||||
| RBAC — 6 roles, 54 permissions | |||||
| Password policy | |||||
| Audit log | |||||
| Secrets encrypted in the database | |||||
| Signed updates | |||||
| Operation without connectivity | |||||
| Administrator account recovery | |||||
| Secret vault | |||||
| Key archival | |||||
| LDAP / Active Directory authentication | |||||
| Active Directory group mapping | |||||
| Full audit and extended retention | |||||
| ANSSI compliance | |||||
| Reporting and exports | |||||
| Dashboard | |||||
| PKI health report | |||||
| Full inventory report | |||||
| Expiry report | |||||
| CSV export | |||||
| Custom report | |||||
| PDF export | |||||
| ANSSI compliance report | |||||
| Reports per authority | |||||
| Consolidated multi-authority dashboard | |||||
| Operations | |||||
| Database backup and restore | |||||
| System monitoring | |||||
| Log management | |||||
| Certificate authority backup | |||||
| Conversion tools (PEM, DER, PFX, P7B) | |||||
| Multi-authority backup | |||||
| System monitoring per authority | |||||
| Integration | |||||
| French / English web interface | |||||
| SMTP notifications | |||||
| SQLite database | |||||
| SQL Server / PostgreSQL | |||||
| External API | |||||
| Licence | |||||
| French / English documentation | |||||
| Updates included | |||||
| Alert before expiry | 30 days | 30 days | 30 days | 30 days | 30 days |
| Grace period | 15 days | 15 days | 15 days | 15 days | 15 days |
Certificates merely discovered in the inventory are not counted: only those placed under monitoring are. An edition can be changed without reinstalling — the licence is a signed file, swapped on a running system.
Frequently asked questions
Frequently asked questions
Other questions? Browse our resources or contact the team.
Does Certyra replace Microsoft ADCS?
No. Certyra complements Microsoft ADCS without replacing it. It adds monitoring, management and traceability on top of your existing infrastructure.
Does data leave the information system?
No. Certyra is a 100% on-premise solution. Your data stays inside your information system and is never sent to a cloud service.
Can several certificate authorities be managed?
Yes, from edition L. Certyra manages one or more authorities within a single Active Directory domain, with a consolidated view and rules tailored to each authority.
Which reports are available?
Certyra provides reports on inventory, expiry, PKI health, ANSSI compliance and the audit log. Reports export to CSV and PDF.
Contact us
Let’s talk about your project
A question, a specific need or a demo request? Our team replies promptly.